


See Wallarm's AI Control Platform In Action
API Security for Google Cloud
Wallarm discovers every API running on Google Cloud and blocks API attacks, bots and abuse in real time. Deploy it on GKE, Compute Engine or alongside Apigee in minutes, and manage it with your existing Google Cloud tools.
What is Wallarm for Google Cloud?
Wallarm for Google Cloud is a deployment of the Wallarm AI Control Platform that protects APIs, web applications, serverless workloads and AI agents running on Google Cloud Platform. A Wallarm Node runs in your GCP project, inspects API traffic inline, and sends only attack metadata to the Wallarm Cloud for analysis. It supports REST, GraphQL, gRPC, WebSocket, JSON and XML traffic.
Deploying Web Apps on GCP
Find every API on GCP
Block attacks in real time
Native to Google Cloud
Data stays in your project
How Wallarm works on Google Cloud
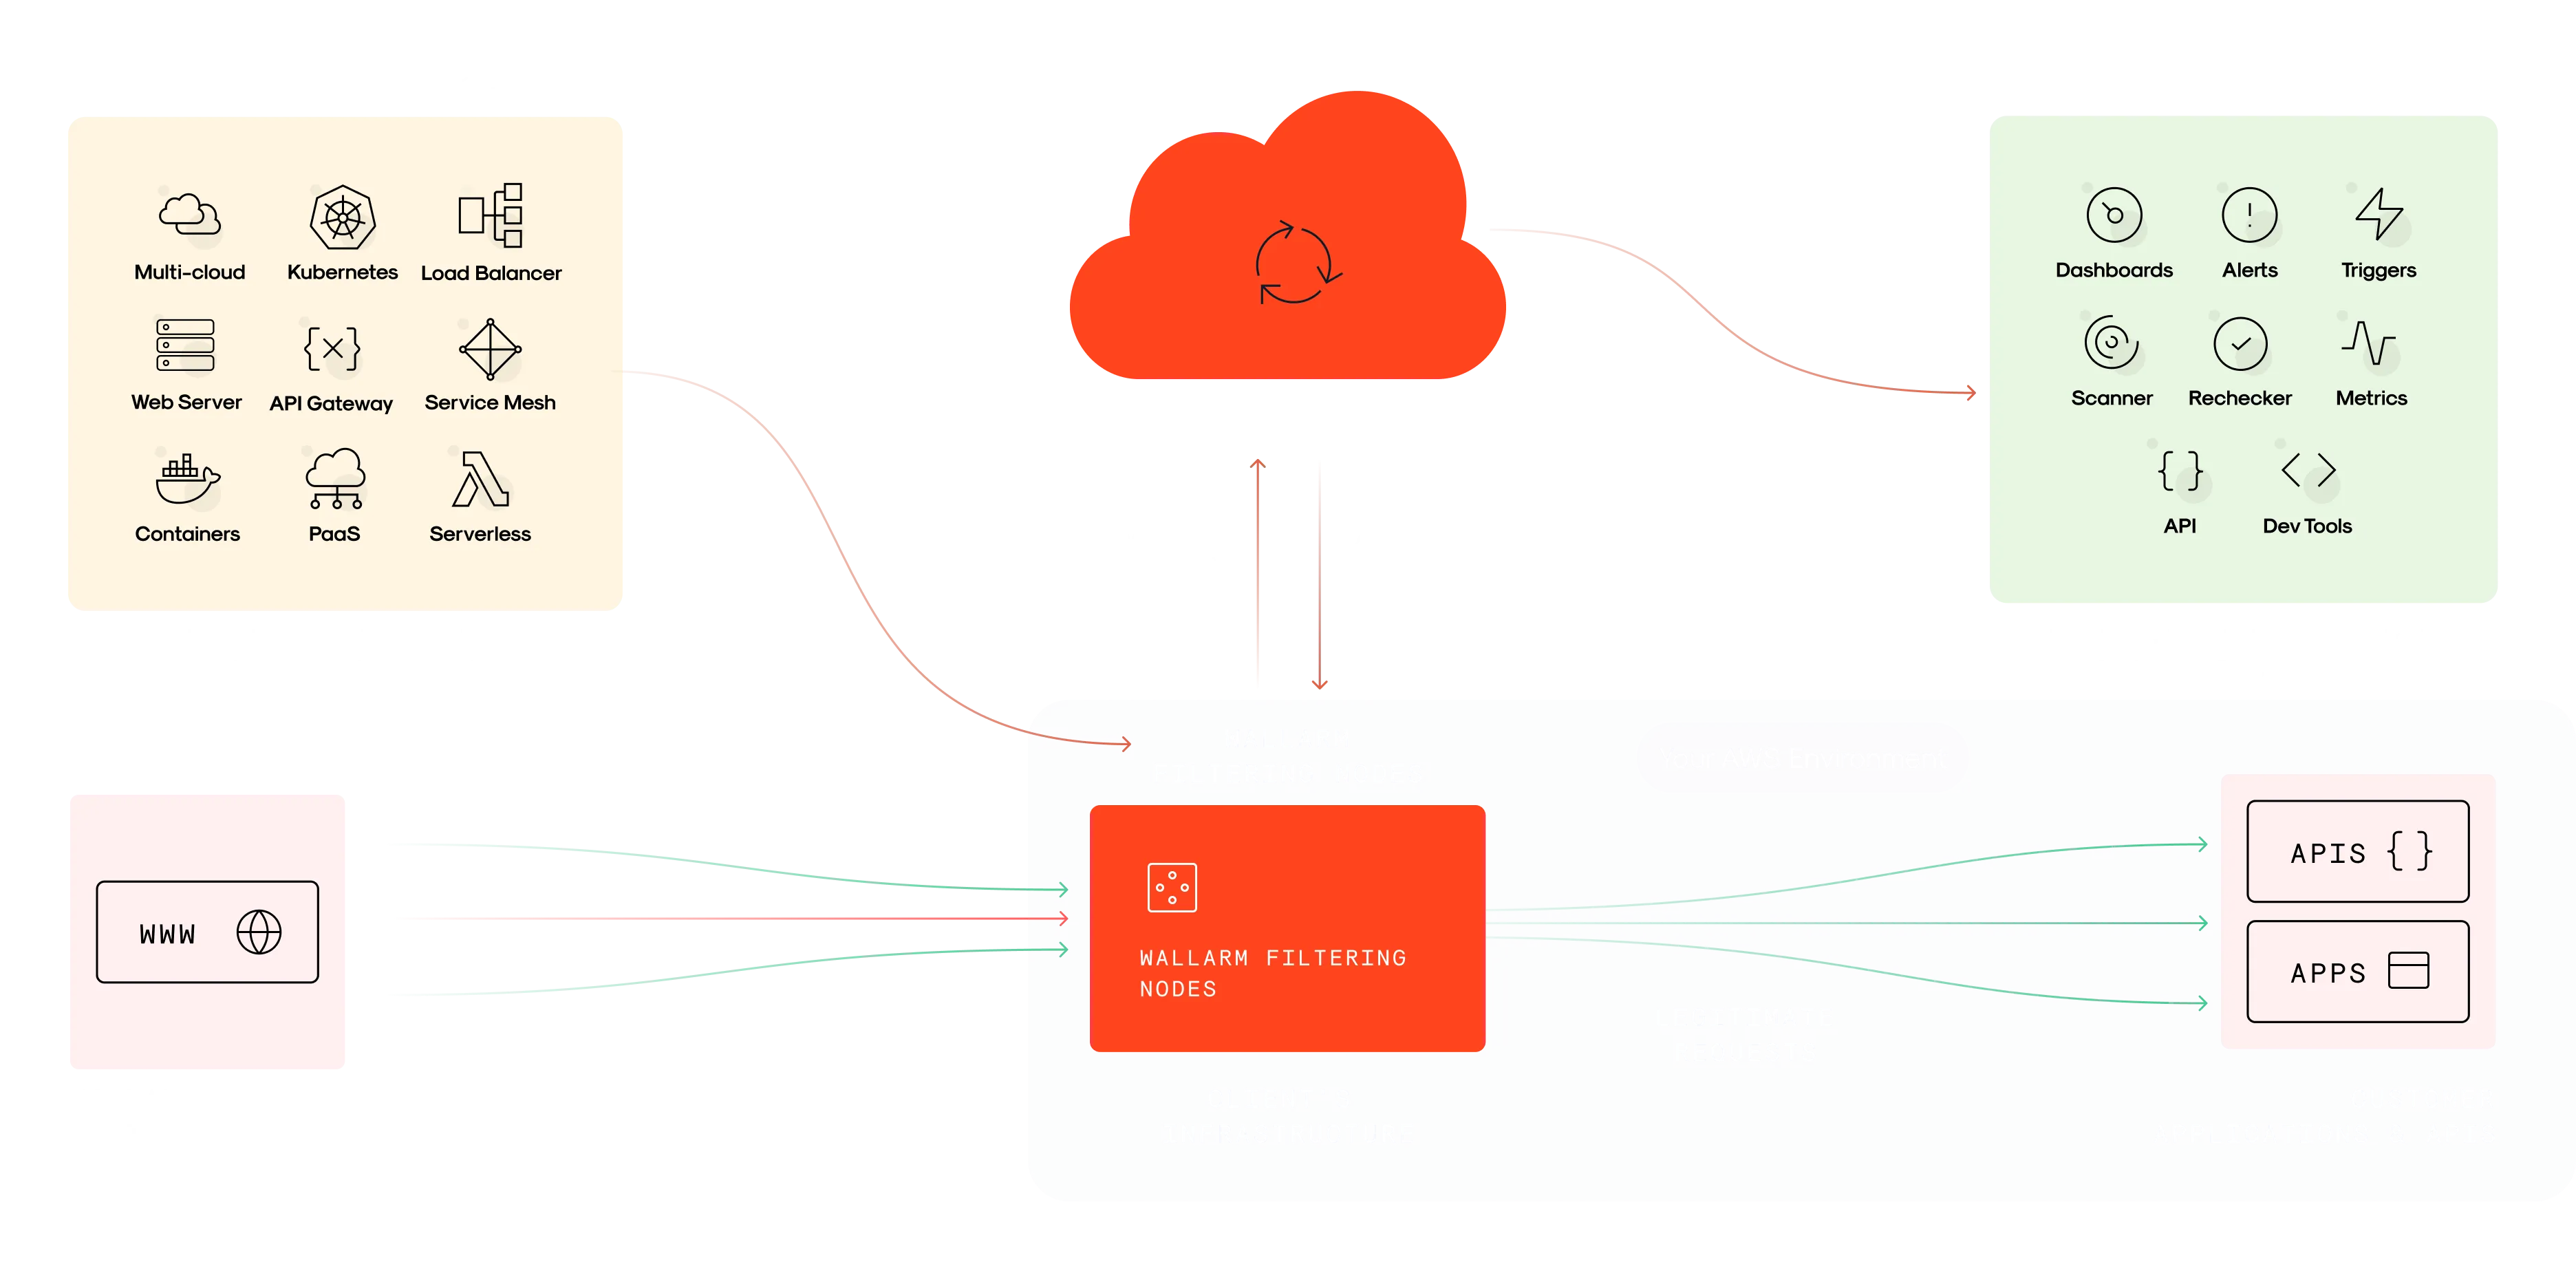
Wallarm Nodes run inline in your Google Cloud project behind Cloud Load Balancing. They filter traffic locally and sync with the Wallarm Cloud for analytics, API inventory and policy updates.
Deployment options on Google Cloud
Google Cloud Machine Image
Docker on Compute Engine
Auto scaling
GKE Ingress Controller
Wallarm vs. Google Cloud Armor:
how they work together
Google Cloud Armor provides DDoS protection and WAF rules at the Google Cloud edge. Wallarm adds API discovery and API-specific attack detection behind it. Most GCP teams run both.
| Capability | Google Cloud Armor | Wallarm |
|---|---|---|
| Where it runs | Google Cloud load balancer edge | Inline in your GCP project (GKE, Compute Engine) or Wallarm Security Edge |
| L3/L4 and volumetric DDoS | Yes | Not the focus; pair with Cloud Armor |
| API inventory and discovery | No | Yes |
| GraphQL, gRPC, WebSocket parsing | Limited | Yes |
| API abuse, bots, business logic attacks | Rate limiting and bot rules | Behavioral detection per endpoint |
| Multi-cloud and on-prem coverage | Google Cloud only | GCP, AWS, Azure, on-prem |
Secure AI agents and LLM APIs on Google Cloud
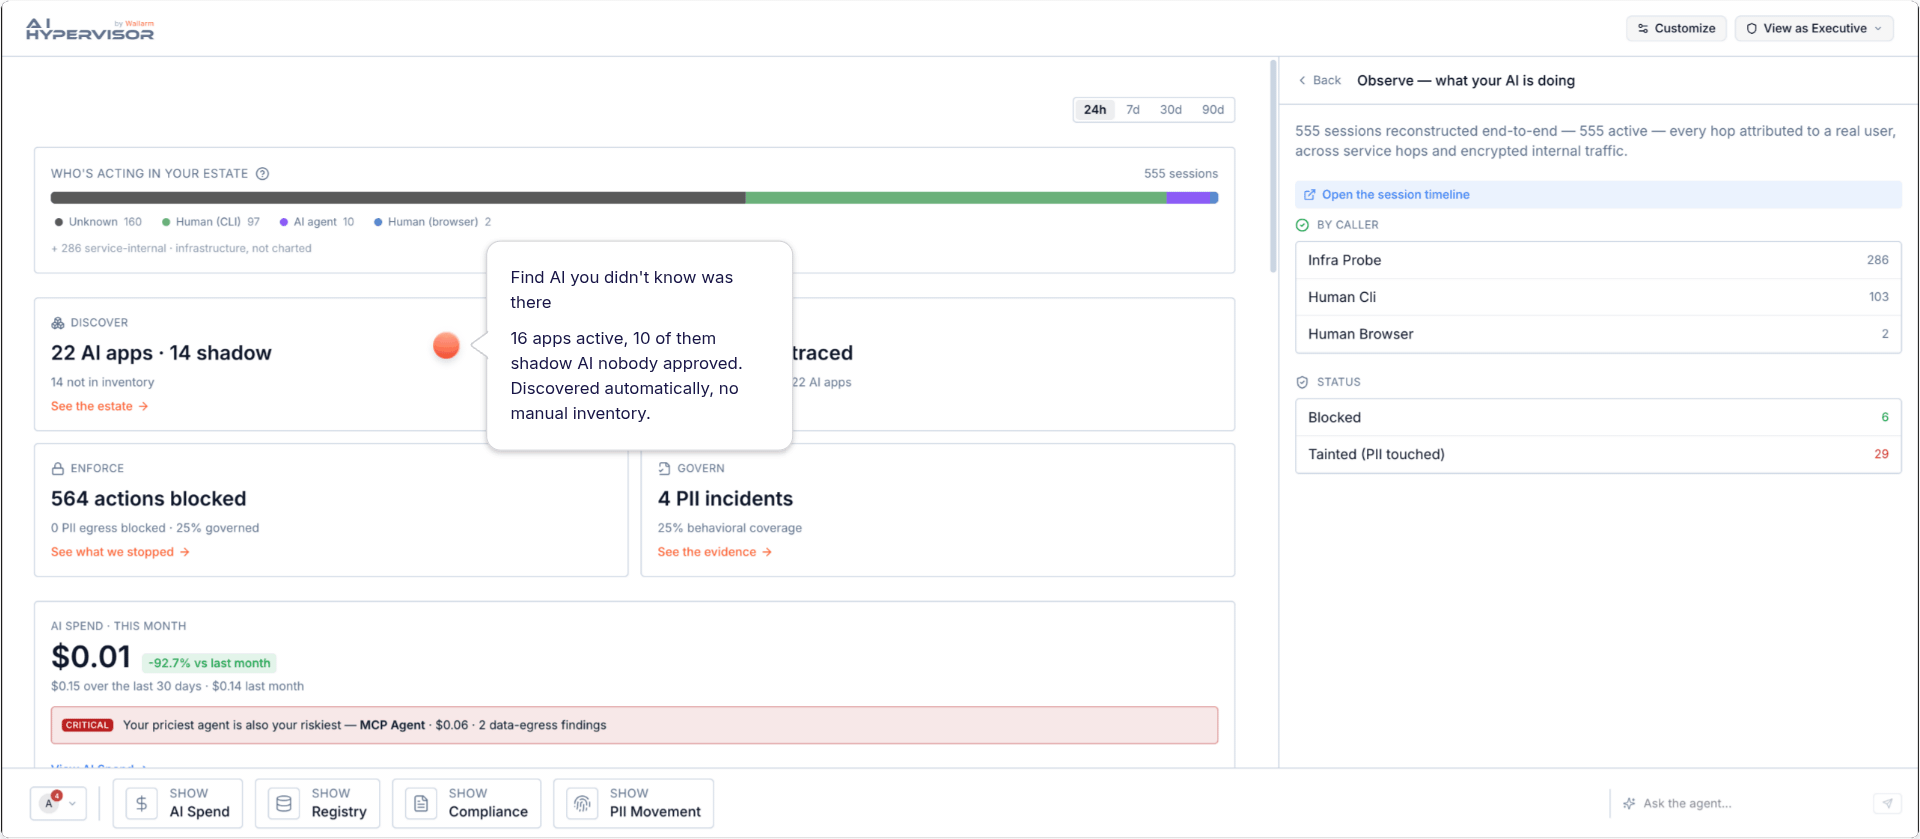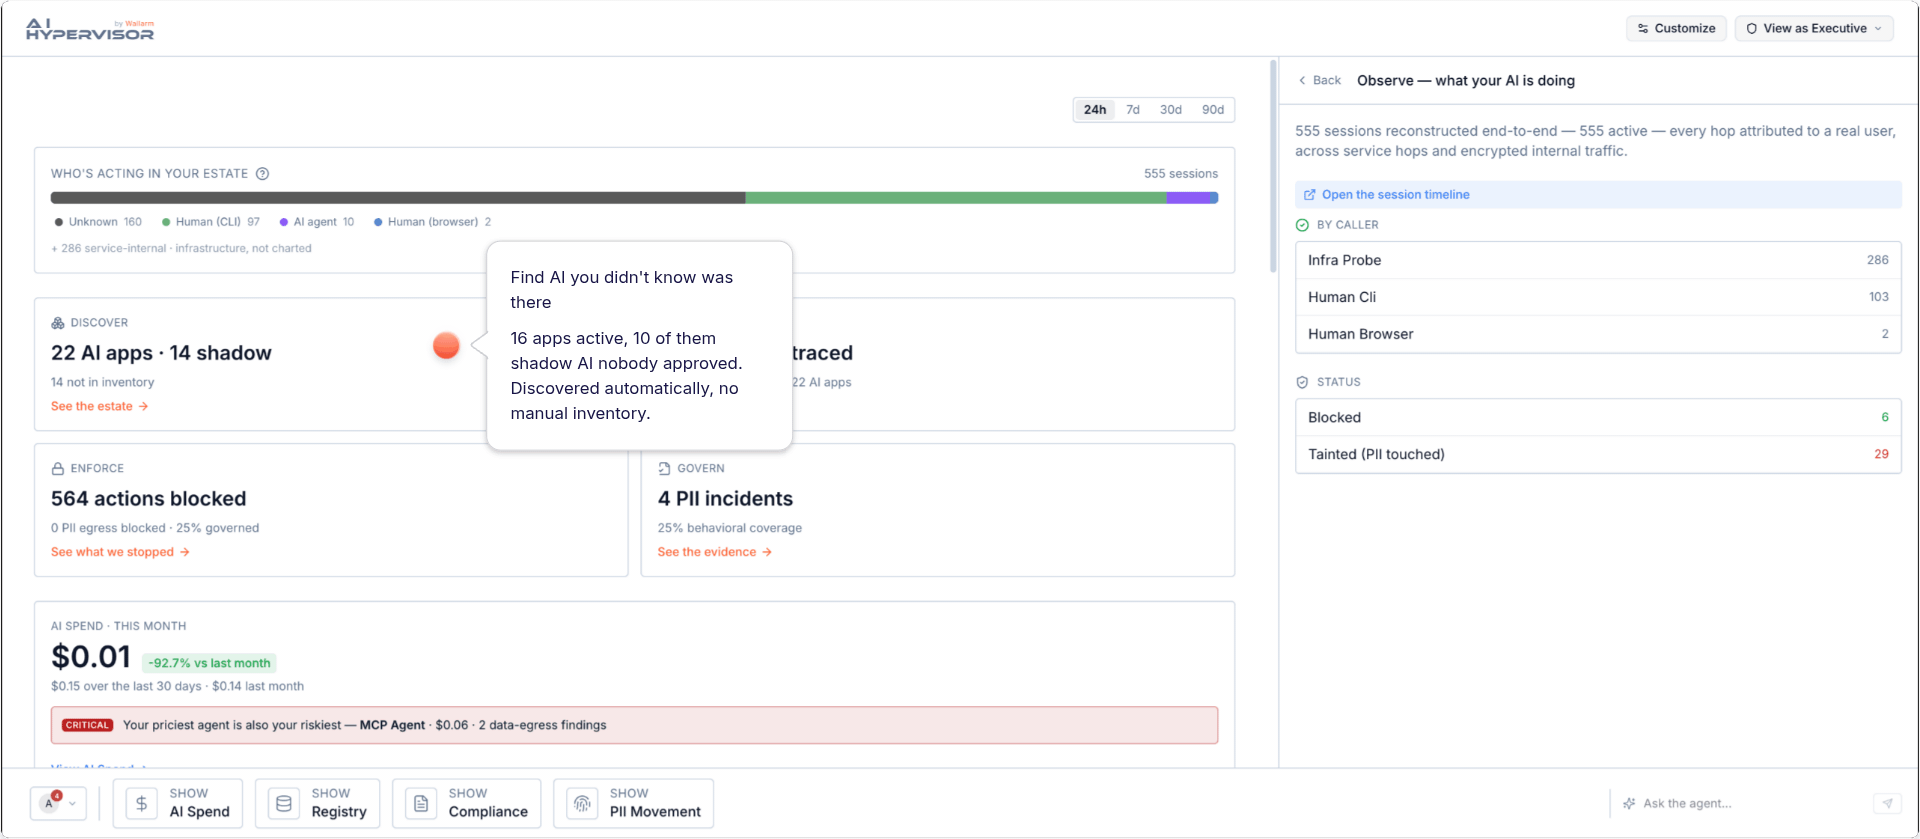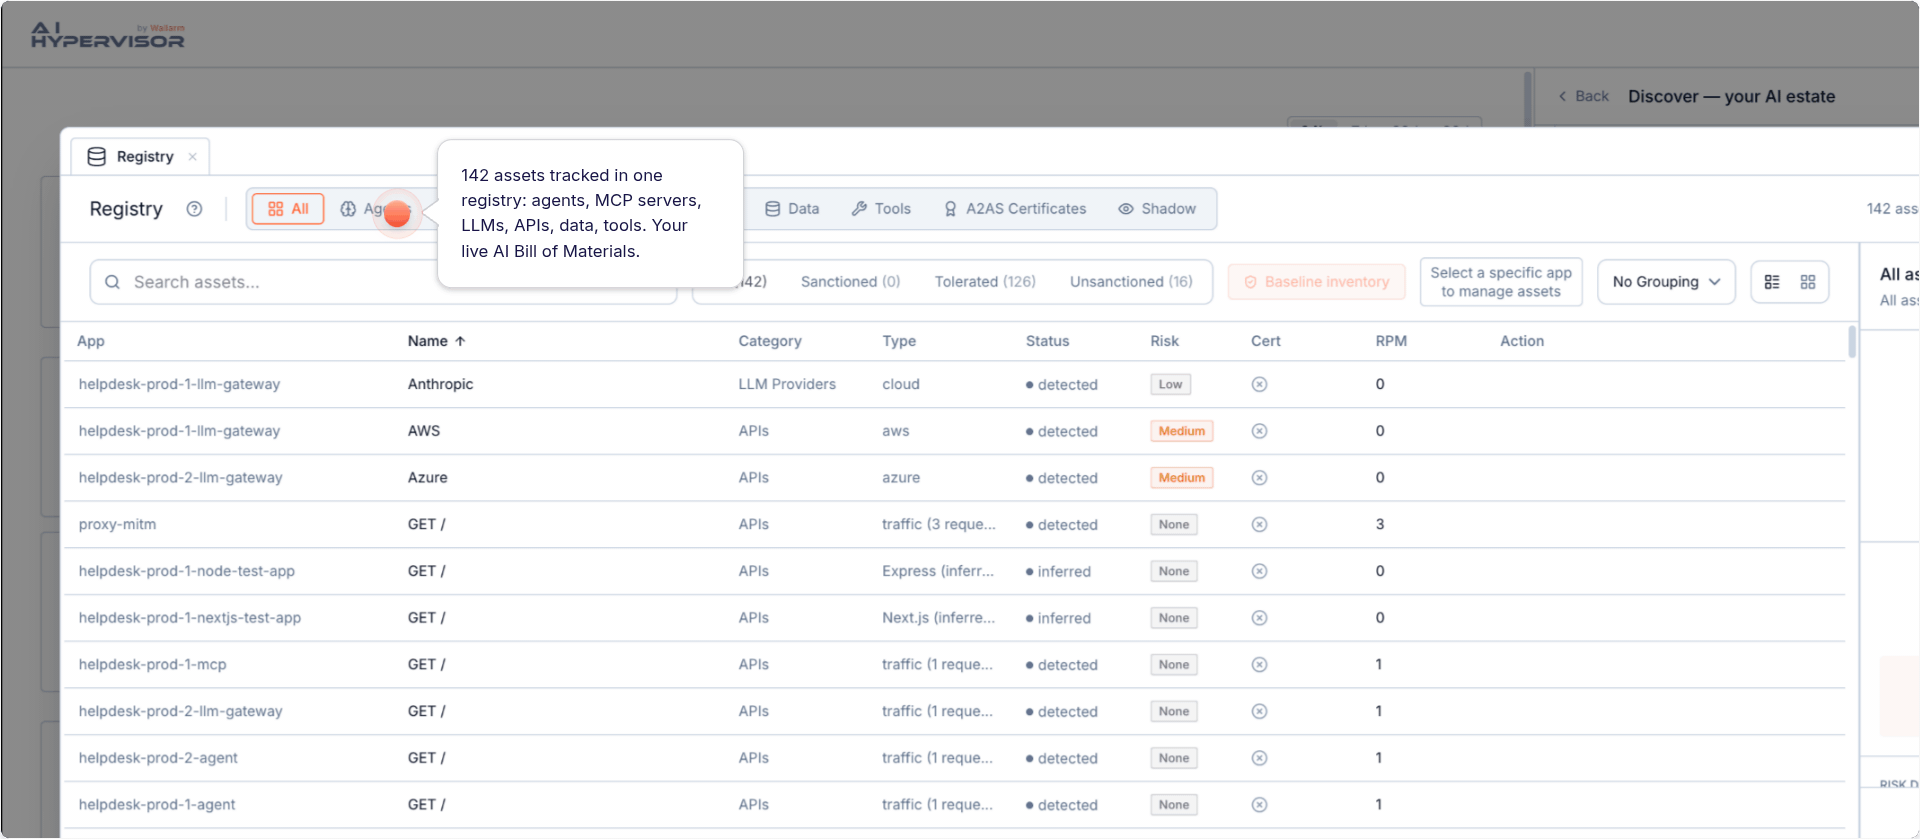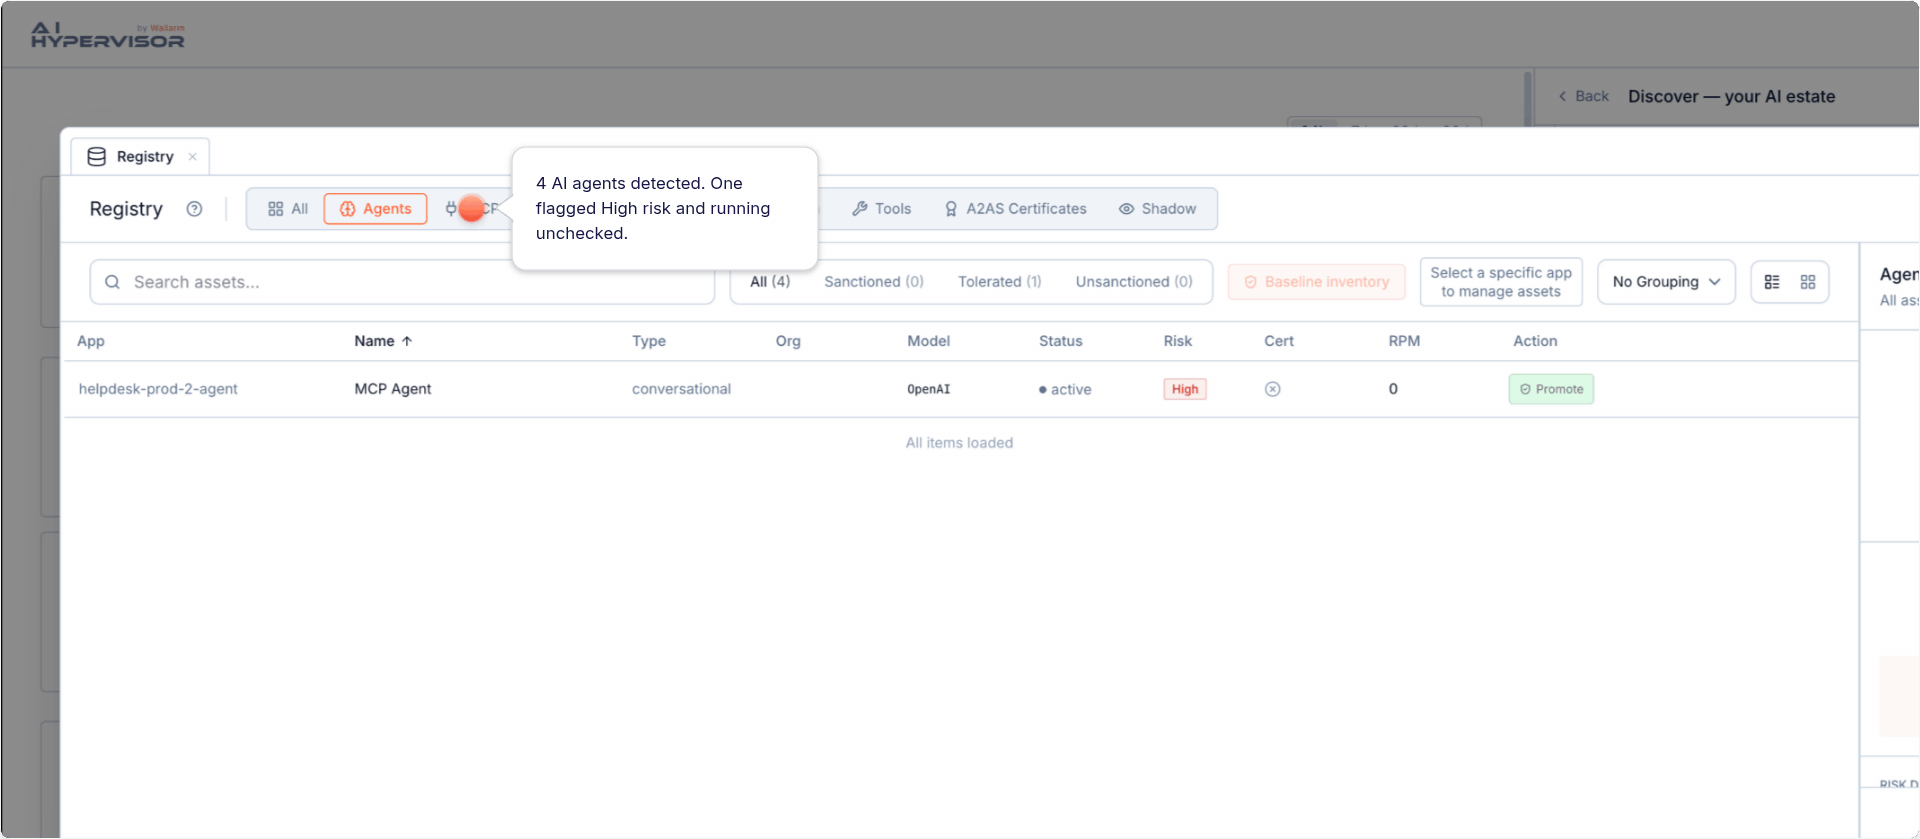
AI agents call APIs. Wallarm sees those calls, maps which agents reach which data, and enforces policy in real time through the Wallarm AI Control Platform.
Trusted by Security.
Attackers don’t care that you watch them, they only care if you stop them. That’s why Wallarm is the preferred choice for Security teams seeking unparalleled protection and prevention capabilities.
#1
In customer reviews [SOURCE TBC: platform + category]
160K+
APIs protected
Billions
of API requests protected daily
With Wallarm, we've been able to scale API protection to the scale we need and manage with our infrastructure-as-code approach.

Frequently asked questions
How do I secure APIs on Google Cloud?
Deploy a Wallarm Node in your GCP project — as a Google Cloud Machine Image, a Docker container on Compute Engine, or an Ingress Controller on GKE. Wallarm then discovers your APIs and blocks attacks inline.
Does Wallarm replace Google Cloud Armor?
No. Cloud Armor handles DDoS and edge WAF rules; Wallarm adds API discovery, API-specific attack detection and abuse prevention. Most teams run Wallarm behind Cloud Armor.
Is Wallarm available on Google Cloud Marketplace?
Yes. The official Wallarm Node Machine Image is listed on Google Cloud Marketplace and launches from the Google Cloud console.
How does Wallarm protect APIs on GKE?
Wallarm deploys to GKE as an NGINX-based Ingress Controller through a Helm chart, or as a sidecar for pod-level protection. It supports ARM64 node pools.
Can Wallarm protect APIs managed in Apigee?
Yes. Wallarm integrates with Apigee to inspect and protect API traffic managed by the gateway.
Does Wallarm scale with GCP traffic?
Yes. You can build a Wallarm Node image and run it in managed instance groups with auto scaling behind Cloud Load Balancing.
Where is my data processed?
Requests are inspected inside your GCP project. Only attack metadata is sent to the Wallarm Cloud, hosted in the US, EU or Middle East region you choose.
Which API protocols does Wallarm support on GCP?
REST, GraphQL, gRPC and WebSocket APIs, with JSON and XML payloads.